Rocky Linux 10.2
Available downloads
Choose the image that matches your architecture and use case.
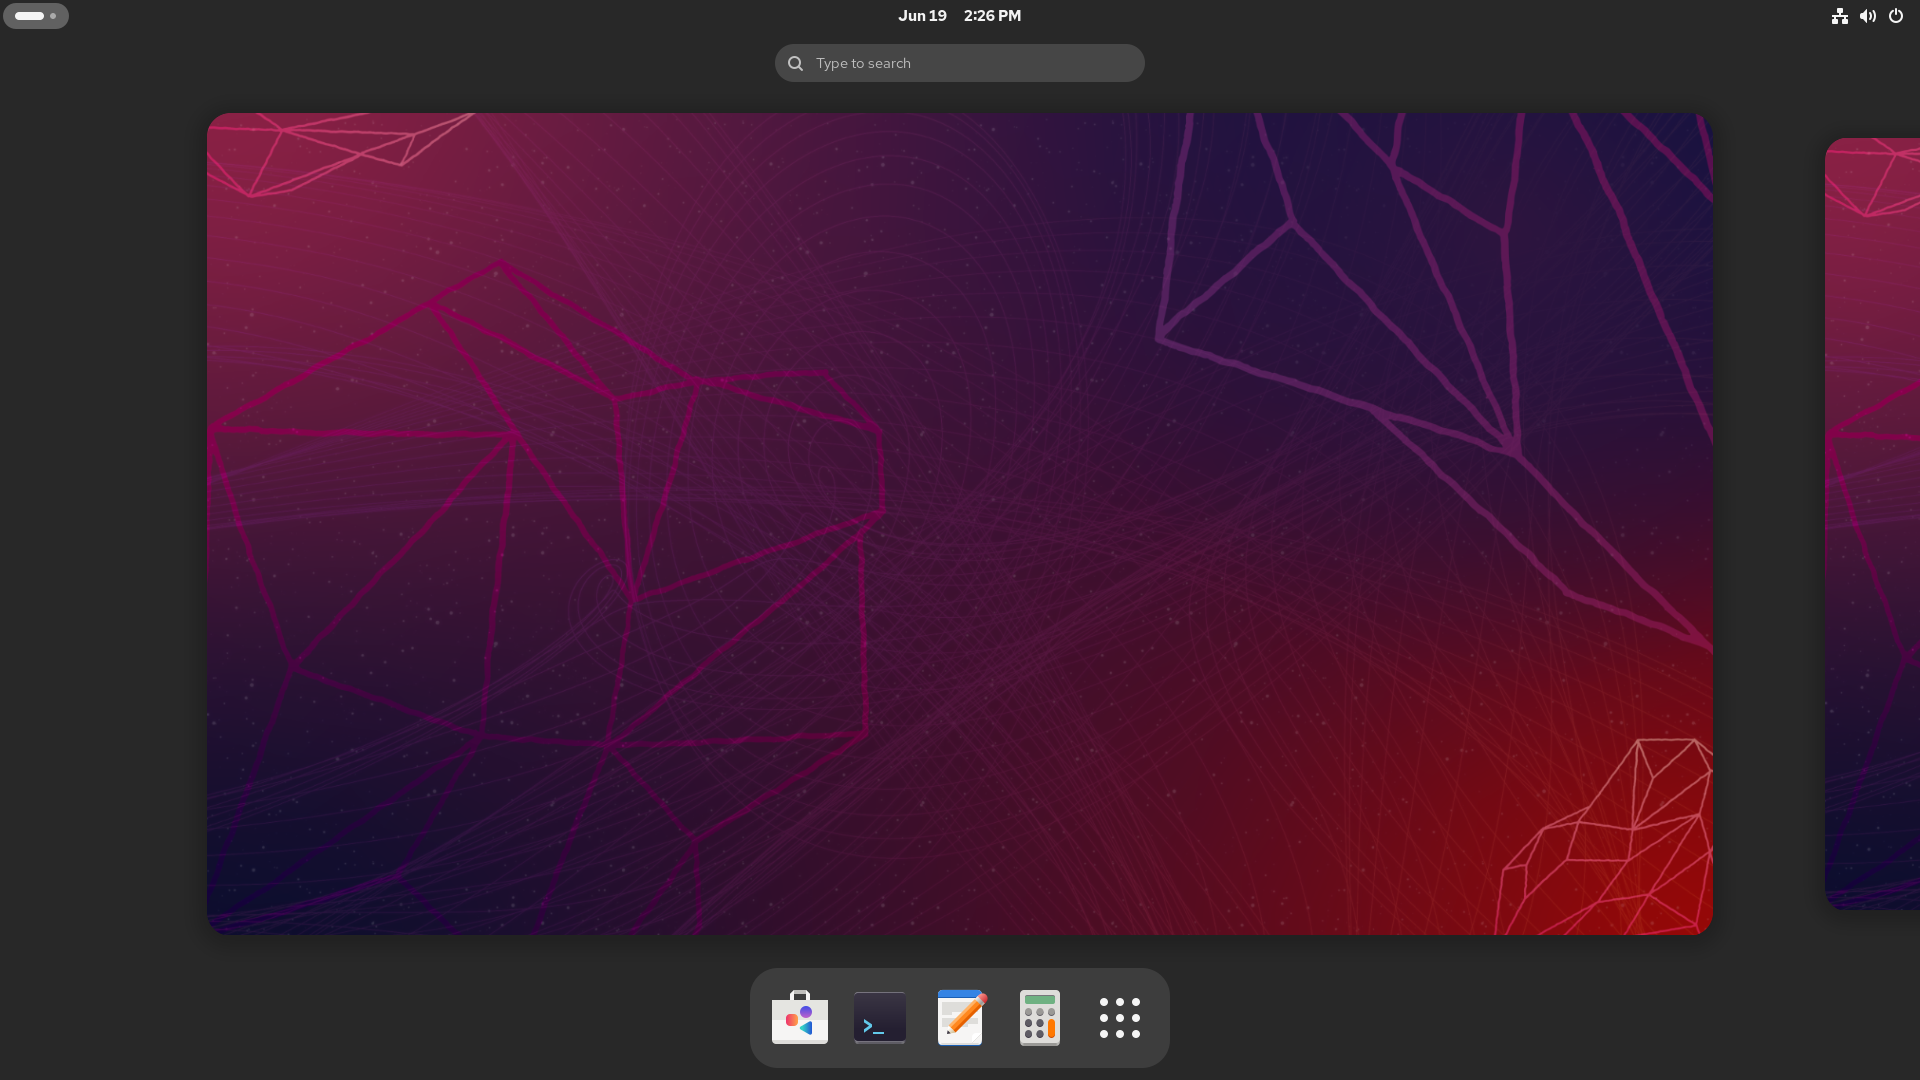
Reference screenshot; point releases may differ. Rocky Enterprise Software Foundation; screenshot by ZalnaRs · Source · GPL-2.0-or-later
Description
Rocky Linux is a community enterprise distribution designed for compatibility with the Red Hat Enterprise Linux ecosystem. Rocky Linux 10.2 is the newest stable branch, with maintained 9 and 8 branches available for long-term server, cloud and workstation use.
Who is Rocky Linux for?
Rocky Linux is primarily suited to daily desktop use, study, web browsing and productivity; servers, virtual machines and self-hosted services; managed infrastructure where predictable maintenance is important. Before choosing it, compare the current release lifecycle with the length of support required for the machine. This distribution is based on rhel, which influences package formats, repositories and much of the available documentation. The listed desktop environment is GNOME; confirm its memory, graphics and accessibility requirements on the official project site. The best choice depends on hardware support, preferred software, update policy and the amount of system administration the user wants to perform.
Before installing
Read the release notes and installation guide before downloading. Select an image that matches the processor architecture and intended use: desktop, server, live media, virtual machine or another published edition. Test Wi-Fi, graphics, audio, storage and suspend from live media when that option is available. Back up important files before repartitioning, encryption changes or dual-boot installation. For production deployment, verify application compatibility, upgrade paths, backup restoration and the project security-support policy in a non-production environment first. Download from an official project page or mirror, compare the published SHA-256 checksum, and verify a signed checksum when the project provides one. After installation, apply updates before adding third-party repositories or drivers.
Advantages
- Offers installation or deployment options intended for server and infrastructure workloads.
- Fits managed environments that value documented maintenance and predictable operational practices.
- Benefits from the package ecosystem and documentation associated with its rhel lineage.
Limitations
- Some repositories, support services or downloads may require registration or a commercial entitlement.
Distribution details
- System type
- linux_distribution
- Based on
- rhel
- Desktop
- GNOME
- Updates
- enterprise
- Categories
- desktop, server, enterprise
Installation requirements
- Architectures
- x86_64_v3aarch64ppc64les390xriscv64
- Memory
- 2 GB minimum; 4 GB recommended
- Storage
- 10 GB minimum; 40 GB recommended
- Firmware
- UEFI or BIOS; x86_64-v3 requires a Haswell-class Intel CPU or equivalent feature level.
Text-mode minimum and GUI recommendation for Rocky Linux 10; production sizing depends on workload.
Safe download
The download button first records an anonymous aggregated download counter and then redirects to the official source.
After installing Rocky Linux
A project-specific post-installation checklist. Commands are displayed for your own equipment; the website never runs them. Use an authorized administrator account when required.
Protect workloads first
Create application-consistent backups and test restoration before package maintenance.
Before you continue: A live copy of database files may be inconsistent.
Read project documentation: Protect workloads firstCheck enabled repositories
Review repositories for the installed Rocky major release.
Before you continue: Investigate unknown third-party repositories.
Read project documentation: Check enabled repositoriesdnf repolistInspect security advisories
Review available security advisory metadata to prioritize fixes.
Before you continue: Missing advisory metadata does not prove there are no vulnerabilities.
Read project documentation: Inspect security advisoriesdnf updateinfo list updates securityApply supported package updates
Review the DNF transaction before confirmation.
Before you continue: Plan service interruption and kernel restart; retain console access.
Read project documentation: Apply supported package updatessudo dnf upgradeKeep SELinux enforcing
Inspect the current mode and investigate policy denials rather than disabling protection.
Before you continue: Do not use permissive mode as a permanent fix.
Read project documentation: Keep SELinux enforcinggetenforceReview active firewall zones
Inspect which interfaces belong to each active zone.
Before you continue: Preserve remote-management access before changing policy.
Read project documentation: Review active firewall zonessudo firewall-cmd --get-active-zonesInspect allowed services
Review the policy for the intended zone before exposing applications.
Before you continue: The default zone is not necessarily every active interface's zone.
Read project documentation: Inspect allowed servicessudo firewall-cmd --list-allValidate the service after maintenance
Test the workload and recovery procedure after updates, not just package-manager success.
Before you continue: Keep backups outside the updated host.
Read project documentation: Validate the service after maintenance